



Silent Lynx Exploits WinRAR Flaw to Deploy Reverse Shell in CIS Government Attacks · 4h NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks · 7h Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing · 8h Drupal Patches Critical Core RCE Flaw with No-Login Path via Contributed Modules · 8h Vulnerability in Sparx Systems Enterprise Architect software · 8h Curl verhelpt 'high' RCE-kwetsbaarheid gevonden door Anthropic · 9h Vulnerabilities in Slican telephone exchanges · 9h Palo Alto Networks waarschuwt voor misbruik van beveiligingslek in firewalls · 13h Cisco meldt actief misbruik van kritiek lek in Secure Email Gateway · 13h Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts · 13h Silent Lynx Exploits WinRAR Flaw to Deploy Reverse Shell in CIS Government Attacks · 4h NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks · 7h Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing · 8h Drupal Patches Critical Core RCE Flaw with No-Login Path via Contributed Modules · 8h Vulnerability in Sparx Systems Enterprise Architect software · 8h Curl verhelpt 'high' RCE-kwetsbaarheid gevonden door Anthropic · 9h Vulnerabilities in Slican telephone exchanges · 9h Palo Alto Networks waarschuwt voor misbruik van beveiligingslek in firewalls · 13h Cisco meldt actief misbruik van kritiek lek in Secure Email Gateway · 13h Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts · 13h
🛡️
ACyber Sentinel Security Assessment Team

Latest Intelligence — Page 21 of 24
[object Object]

[object Object]

BackgroundDarkMe, a Visual Basic 6 (VB6) spy trojan and remote access tool became well known in February 2024 for its use of zero days to deliver malware. But t...
📰 Huntress 🕐 Sep 22
Check Point Warns of Management Server Zero-Day Exploited in Targeted Attacks

Check Point Warns of Management Server Zero-Day Exploited in Targeted Attacks

Attackers exploited a previously unknown flaw in Check Point's Security Management Server in a handful of targeted attacks on July 23, the company said. The fla...
📰 The Hacker News 🕐 Sep 22
WordPress Issues Patch for Critical Flaw That Can Enable Code Execution on Some Servers

WordPress Issues Patch for Critical Flaw That Can Enable Code Execution on Some Servers

WordPress has fixed a critical flaw in its core software that lets an attacker with no account make a site load a PHP file from outside its theme folders. On so...
📰 The Hacker News 🕐 Sep 22
Critical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without Credentials

Critical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without Credentials

A critical vulnerability in Bifrost, an open-source AI gateway that routes requests to more than 20 LLM providers, allows an unauthenticated attacker to run arb...
📰 The Hacker News 🕐 Sep 22
Researcher Drops BigDiskBuster Zero-Day PoC That Blocks Microsoft Defender Updates

Researcher Drops BigDiskBuster Zero-Day PoC That Blocks Microsoft Defender Updates

A zero-day proof-of-concept tool that stops Microsoft Defender from installing platform and signature updates by filling all available disk space was published ...
📰 The Hacker News 🕐 Sep 22
D-Link waarschuwt voor kritieke kwetsbaarheid in wifi-router

D-Link waarschuwt voor kritieke kwetsbaarheid in wifi-router

D-Link waarschuwt voor een kritieke kwetsbaarheid in de DIR-822A wifi-routers waar op dit moment nog geen patch voor beschikbaar is. De kwetsbaarheid (CVE-2026-...
📰 security.nl 🕐 Sep 22
MikroTrick: technical analysis, disclosure process, and the use of LLM agents

MikroTrick: technical analysis, disclosure process, and the use of LLM agents

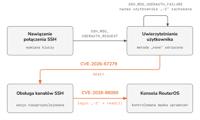
Introduction On 3 September 2026, MikroTik released patches almost simultaneously for several maintained RouterOS branches: 7.25beta3, 7.24.2, 7.23.4, and 6.49....
📰 cert.pl 🕐 Sep 22
New CVSS 10.0 VeloCloud Orchestrator Flaw Actively Exploited in Certificate-Based Setups

New CVSS 10.0 VeloCloud Orchestrator Flaw Actively Exploited in Certificate-Based Setups

Attackers are exploiting a new flaw in on-premises VeloCloud Orchestrator (VCO), the server that manages the Edge devices in a VeloCloud SD-WAN, Arista said on ...
📰 The Hacker News 🕐 Sep 22
New Linux Kernel Flaw Gives ARM64 KVM Guests Read-Write Access to Host Memory

New Linux Kernel Flaw Gives ARM64 KVM Guests Read-Write Access to Host Memory

A new flaw in the Linux kernel's KVM virtualization code for ARM64 processors can leave a freed piece of host memory exposed to a guest virtual machine on hosts...

📰 The Hacker News 🕐 Sep 22