CVE-2026-67276 - SSH user impersonation possible in Mikrotik RouterOS
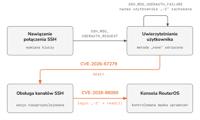
RouterOS does not compare the complete RSA public key when matching an SSH authentication request to an authorized user key, checking the key type and modulus but omitting the exponent. Because signature verification uses the client-supplied key, an attacker knowing an authorized RSA modulus can supply a key with exponent one, forge a valid signature, and open an SSH command channel as the target user without the private key.This issue affects only 7.x branch was fixed in versions: 7.23.4 (Long-term) and 7.24.2 (Stable)
Опубликовано: Sep 05, 2026 20:17
Изменено: Sep 25, 2026 14:57