CVE-2026-67277 - MikroTik RouterOS Missing Authentication for Critical Function Vulnerability - [Actively Exploited]
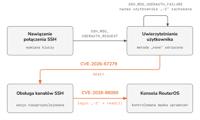
RouterOS accepts a "related" btest connection before the corresponding primary session has completed authentication. An unauthenticated client can use this state to start an IPv4 UDP test. With "random-data=false", the sender transmits an uninitialized tail from a kernel packet buffer. A separate unchecked, inverted packet-size interval causes unsigned integer underflow, anomalously large fragmented output, and can restart the RouterOS kernel.
This issue was fixed in versions: 6.49.21 (Long-term), 7.23.4 (Long-term) and 7.24.2 (Stable)
发布于: Sep 05, 2026 20:17
最后修改: Sep 11, 2026 12:52