CVE-2026-67279 - Mikrotik RouterOS Improper Enforcement of Behavioral Workflow Vulnerability - [Actively Exploited]
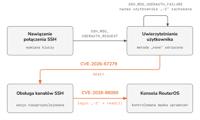
RouterOS SSH enters the connection protocol after a client-requested rekey even though user authentication was never attempted, allowing an unauthenticated client to open a session channel and send an exec request. On affected builds the server dispatches the command, enabling unauthenticated creation, overwrite, and reconstruction of files in the RouterOS managed file namespace, including support files containing configuration and diagnostic data.This issue was fixed in versions: 6.49.21 (Long-term), 7.23.4 (Long-term) and 7.24.2 (Stable)
Published: Sep 05, 2026 20:17
Last Modified: Sep 26, 2026 04:17