CVE-2026-86060 - MikroTik RouterOS Improper Neutralization of Argument Delimiters in a Command Vulnerability - [Actively Exploited]
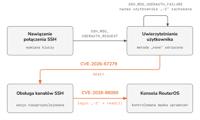
RouterOS contains an argument-handling flaw in the SSH login
path involving usernames that begin with a prohibited character, allowing for the trusted RouterOS policy mask to be changed, leading to privilege escalation. Exploitation requires an unauthenticated SSH session to reach the RouterOS login helper.This issue was fixed in versions: 6.49.21 (Long-term), 7.23.4 (Long-term) and 7.24.2 (Stable)
انتشار: Sep 05, 2026 20:17
آخرین تغییر: Sep 11, 2026 12:52