Silent Lynx Exploits WinRAR Flaw to Deploy Reverse Shell in CIS Government Attacks · 4h NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks · 7h Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing · 8h Drupal Patches Critical Core RCE Flaw with No-Login Path via Contributed Modules · 8h Vulnerability in Sparx Systems Enterprise Architect software · 8h Curl verhelpt 'high' RCE-kwetsbaarheid gevonden door Anthropic · 9h Vulnerabilities in Slican telephone exchanges · 9h Palo Alto Networks waarschuwt voor misbruik van beveiligingslek in firewalls · 13h Cisco meldt actief misbruik van kritiek lek in Secure Email Gateway · 13h Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts · 13h Silent Lynx Exploits WinRAR Flaw to Deploy Reverse Shell in CIS Government Attacks · 4h NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks · 7h Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing · 8h Drupal Patches Critical Core RCE Flaw with No-Login Path via Contributed Modules · 8h Vulnerability in Sparx Systems Enterprise Architect software · 8h Curl verhelpt 'high' RCE-kwetsbaarheid gevonden door Anthropic · 9h Vulnerabilities in Slican telephone exchanges · 9h Palo Alto Networks waarschuwt voor misbruik van beveiligingslek in firewalls · 13h Cisco meldt actief misbruik van kritiek lek in Secure Email Gateway · 13h Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts · 13h
🛡️
ACyber Sentinel Security Assessment Team

Latest Intelligence — Page 13 of 15
Critical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without Credentials

Critical Bifrost AI Gateway Flaw Lets Attackers Run Commands Without Credentials

A critical vulnerability in Bifrost, an open-source AI gateway that routes requests to more than 20 LLM providers, allows an unauthenticated attacker to run arb...
📰 The Hacker News 🕐 Sep 22
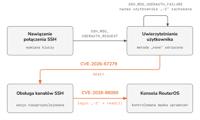
MikroTrick: technical analysis, disclosure process, and the use of LLM agents

MikroTrick: technical analysis, disclosure process, and the use of LLM agents

Introduction On 3 September 2026, MikroTik released patches almost simultaneously for several maintained RouterOS branches: 7.25beta3, 7.24.2, 7.23.4, and 6.49....
📰 cert.pl 🕐 Sep 22
SharePoint Flaw Initially Listed as Spoofing by Microsoft Enables Authenticated RCE

SharePoint Flaw Initially Listed as Spoofing by Microsoft Enables Authenticated RCE

A SharePoint Server vulnerability that Microsoft initially classified as a spoofing flaw with a CVSS score of 6.5 actually enables authenticated remote code exe...
📰 The Hacker News 🕐 Sep 22
Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access

Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a now-patched security flaw impacting Zyxel GS1900 series switches to its Known...
📰 The Hacker News 🕐 Sep 22
ShinyHunters Hacked Clop. Now What About Clop's Victims?

ShinyHunters Hacked Clop. Now What About Clop's Victims?

4 Min ReadSource: winhorse via Getty ImagesShinyHunters apparently breached rival ransomware gang Clop last week, and the incident could pose additional risks t...

📰 Dark Reading 🕐 Sep 21
Weekly ALL-SOURCE Cyber Warfare Intelligence Brief 9.21.26

Weekly ALL-SOURCE Cyber Warfare Intelligence Brief 9.21.26

Reporting period: September 14–21, 2026Assessment cutoff: September 21, 2026Scope: State and state-aligned cyber operations, APT campaigns, technical intelligen...
📰 Krypt3ia 🕐 Sep 21
⚡ Weekly Recap: Cisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser Hijacks

⚡ Weekly Recap: Cisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser Hijacks

A browser. A plugin. A package. A login screen. Normal stuff. That is basically the problem this week. The trouble keeps showing up inside things people already...
📰 The Hacker News 🕐 Sep 21
Claude Opus 5 Helped Researchers Take Over OpenAI Staff Accounts via Chained Flaws

Claude Opus 5 Helped Researchers Take Over OpenAI Staff Accounts via Chained Flaws

Three researchers at the security firm Hacktron used Anthropic's Claude Opus 5 to chain two flaws and take over the ChatGPT and Codex accounts of several OpenAI...
📰 The Hacker News 🕐 Sep 19
SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE

SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE

SolarWinds has released security updates to address a high-severity flaw in Access Rights Manager (ARM) that, if successfully exploited, could lead to an unauth...

📰 The Hacker News 🕐 Sep 19