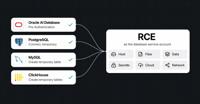



Researcher Demonstrates Database RCE Exploits Affecting PostgreSQL, MySQL and Oracle · 2h CISA Warns of 4 Exploited Flaws Linked to Ransomware, Cryptomining, and LLMjacking Attacks · 3h PHP Warns of Critical Security Flaws Affecting All Supported Versions, Fixes Coming November 19 · 6h 10-Year-Old NGINX HTTP/2 Flaw Lets Unauthenticated Attackers Execute Code on Servers · 16h F5 Warns 6 Critical BIG-IP Flaws Can Crash Traffic in Specific Setups, May Allow RCE · 16h CVE-2026-123633 and CVE-2026-123007: Critical NGINX HTTP/2 Vulnerabilities · 17h Critical Apache Roller RCE Flaw Under Active Exploitation, No Authentication Required · 17h Java4Shell Flaw Threatens Global Enterprises, Java Application Ecosystem · 18h How Cloudflare WAF helps protect against Java4Shell (CVE-2026-114938) · 20h Vulnerabilities in LMS software · 22h Researcher Demonstrates Database RCE Exploits Affecting PostgreSQL, MySQL and Oracle · 2h CISA Warns of 4 Exploited Flaws Linked to Ransomware, Cryptomining, and LLMjacking Attacks · 3h PHP Warns of Critical Security Flaws Affecting All Supported Versions, Fixes Coming November 19 · 6h 10-Year-Old NGINX HTTP/2 Flaw Lets Unauthenticated Attackers Execute Code on Servers · 16h F5 Warns 6 Critical BIG-IP Flaws Can Crash Traffic in Specific Setups, May Allow RCE · 16h CVE-2026-123633 and CVE-2026-123007: Critical NGINX HTTP/2 Vulnerabilities · 17h Critical Apache Roller RCE Flaw Under Active Exploitation, No Authentication Required · 17h Java4Shell Flaw Threatens Global Enterprises, Java Application Ecosystem · 18h How Cloudflare WAF helps protect against Java4Shell (CVE-2026-114938) · 20h Vulnerabilities in LMS software · 22h
🛡️
ACyber Sentinel Security Assessment Team

Latest Intelligence — Page 32 of 51
Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control

Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control

Two of 31 newly disclosed flaws in Progress Software's MarkLogic Server database could let an account given only some management privileges take administrator c...
📰 The Hacker News 🕐 Oct 13
GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code

GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code

GitLab has released patches for a maximum-severity security flaw impacting its Community Edition (CE) and Enterprise Edition (EE) software that could result in ...
📰 The Hacker News 🕐 Oct 13
Maximum-Severity SSRF Flaw in SonicWall SMA Devices Under Attack

Maximum-Severity SSRF Flaw in SonicWall SMA Devices Under Attack

Rob Wright,Senior News Director,Dark ReadingOctober 12, 20264 Min ReadSource: Michael Vi via Alamy Stock PhotoSonicWall customers are on the defensive once agai...
📰 Dark Reading 🕐 Oct 12
⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More

⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More

Some meetings last longer than it took attackers to jump on a newly disclosed security flaw this week. Within hours, they were already testing it. That's not mu...
📰 The Hacker News 🕐 Oct 12
CVE-2026-97229: Critical GitLab Vulnerability Could Allow Remote Code Execution

CVE-2026-97229: Critical GitLab Vulnerability Could Allow Remote Code Execution

October 12, 2026GitLab has addressed CVE-2026-97229, a critical vulnerability in its CI/CD Regular Expression Compiler that could allow an unauthenticated attac...
📰 TheCyberThrone 🕐 Oct 12
Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch

Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch

Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of p...
📰 The Hacker News 🕐 Oct 12
Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE

Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE

A maximum-severity security flaw impacting the Bricksforge plugin for WordPress has come under active exploitation in the wild, according to Patchstack. The cri...
📰 The Hacker News 🕐 Oct 12
CyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records

CyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records

Cybersecurity researchers have disclosed details of a two-pronged artificial intelligence (AI)-augmented initial access campaign targeting WordPress sites, e-co...
📰 The Hacker News 🕐 Oct 12
P7 DarkSword iOS Exploit Kit Adds Crypto Wallet Data Theft and Remote Commands

P7 DarkSword iOS Exploit Kit Adds Crypto Wallet Data Theft and Remote Commands

Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword. "Compared with the variant...

📰 The Hacker News 🕐 Oct 09