



Silent Lynx Exploits WinRAR Flaw to Deploy Reverse Shell in CIS Government Attacks · 3h NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks · 6h Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing · 7h Drupal Patches Critical Core RCE Flaw with No-Login Path via Contributed Modules · 7h Vulnerability in Sparx Systems Enterprise Architect software · 7h Curl verhelpt 'high' RCE-kwetsbaarheid gevonden door Anthropic · 8h Vulnerabilities in Slican telephone exchanges · 8h Palo Alto Networks waarschuwt voor misbruik van beveiligingslek in firewalls · 12h Cisco meldt actief misbruik van kritiek lek in Secure Email Gateway · 12h Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts · 12h Silent Lynx Exploits WinRAR Flaw to Deploy Reverse Shell in CIS Government Attacks · 3h NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks · 6h Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing · 7h Drupal Patches Critical Core RCE Flaw with No-Login Path via Contributed Modules · 7h Vulnerability in Sparx Systems Enterprise Architect software · 7h Curl verhelpt 'high' RCE-kwetsbaarheid gevonden door Anthropic · 8h Vulnerabilities in Slican telephone exchanges · 8h Palo Alto Networks waarschuwt voor misbruik van beveiligingslek in firewalls · 12h Cisco meldt actief misbruik van kritiek lek in Secure Email Gateway · 12h Langflow's Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts · 12h
🛡️
ACyber Sentinel Security Assessment Team

Latest Intelligence — Page 4 of 24
Attacker Chains Three Ivanti Connect Secure Zero-Days for Root Access, Only Two Patched So Far

Attacker Chains Three Ivanti Connect Secure Zero-Days for Root Access, Only Two Patched So Far

An attacker chained three zero-day flaws in Ivanti Connect Secure, a VPN appliance, to run commands as root without logging in, security firm Volexity said on O...
📰 The Hacker News 🕐 2d
SAP Discloses Critical CVSS 10 Flaw in Cloud SDK for Python Allowing OAuth2 Credential Theft

SAP Discloses Critical CVSS 10 Flaw in Cloud SDK for Python Allowing OAuth2 Credential Theft

A flaw in SAP's Cloud SDK for Python can send an application's OAuth2 client credentials to a server an attacker controls, SAP said in a security advisory on Oc...
📰 The Hacker News 🕐 2d
Ivanti waarschuwt voor misbruik van lek in Connect Secure vpn-servers

Ivanti waarschuwt voor misbruik van lek in Connect Secure vpn-servers

Ivanti waarschuwt klanten voor actief misbruik van een kwetsbaarheid in Ivanti Connect Secure vpn-servers. Via het beveiligingslek (CVE-2026-104935) kan een ong...
📰 security.nl 🕐 2d
Franse overheid adviseert supermarkten om koelsystemen offline te halen

Franse overheid adviseert supermarkten om koelsystemen offline te halen

De Franse overheid adviseert supermarkten en andere bedrijven om hun koelsystemen offline te halen. In het geval van gehackte koelinstallaties wordt aangeraden ...
📰 security.nl 🕐 2d
Vulnerability in Payload CMS software

Vulnerability in Payload CMS software

Vulnerability in Payload CMS software CVE ID CVE-2026-63316 Publication date 13 October 2026 Vendor Payload Product Payload CMS Vulnerable versions All before 3...
📰 cert.pl 🕐 2d
GitLab waarschuwt voor kritiek beveiligingslek met CVSS 10.0-score

GitLab waarschuwt voor kritiek beveiligingslek met CVSS 10.0-score

GitLab waarschuwt ontwikkelaars en organisaties voor een kritieke kwetsbaarheid in de software die een CVSS-impactscore van 10.0 op een schaal van 1 tot en met ...
📰 security.nl 🕐 2d
Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers

Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers

Attackers took remote control of fridges and freezers at hundreds of French supermarkets on the night of October 11 and warmed them, forcing stores to throw foo...
📰 The Hacker News 🕐 2d
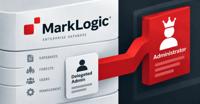
Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control

Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control

Two of 31 newly disclosed flaws in Progress Software's MarkLogic Server database could let an account given only some management privileges take administrator c...
📰 The Hacker News 🕐 2d
GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code

GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code

GitLab has released patches for a maximum-severity security flaw impacting its Community Edition (CE) and Enterprise Edition (EE) software that could result in ...

📰 The Hacker News 🕐 2d